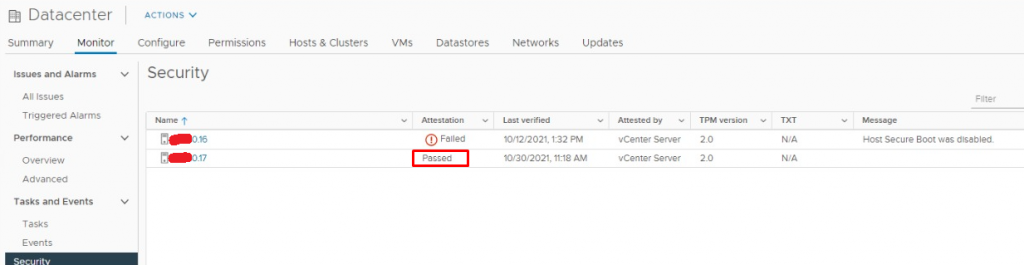
ESXi hosts use Trusted Platform Modules (TPM) chips, which are secure cryptographic processors that increase host security by providing a hardware-based assurance of trust rather than software.
If using the TPM, the following system requirements must be met.
- vCenter Server 6.7 or later
- ESXi 6.7 host or later with TPM 2.0 chip installed and enabled in UEFI
- UEFI Secure Boot enabled
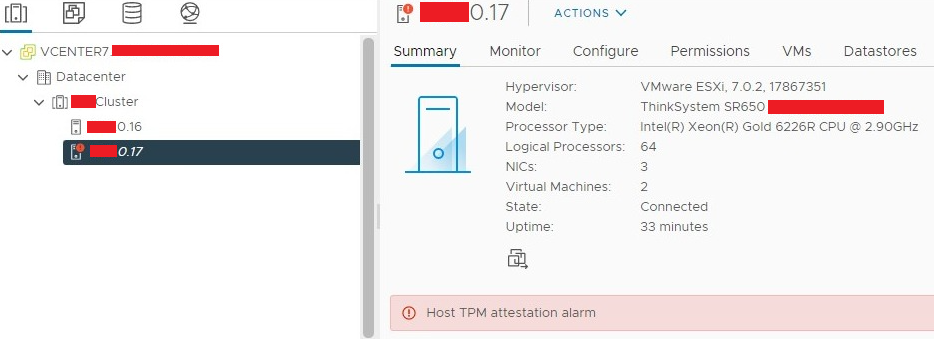
We can see the details of the alarm on the Datacenter monitor screen.
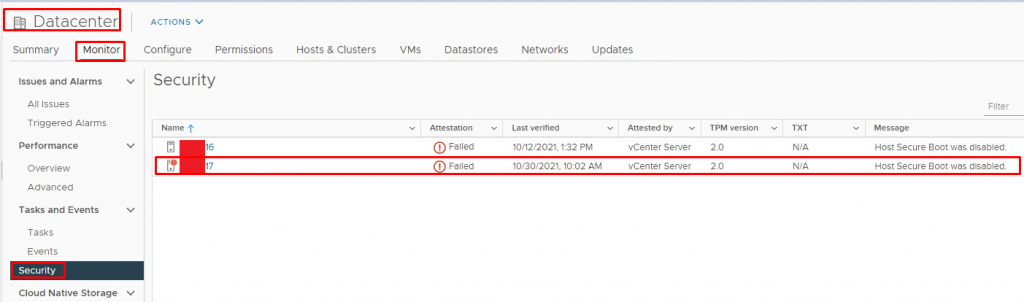
We see that the error we encounter is secure boot disabled.
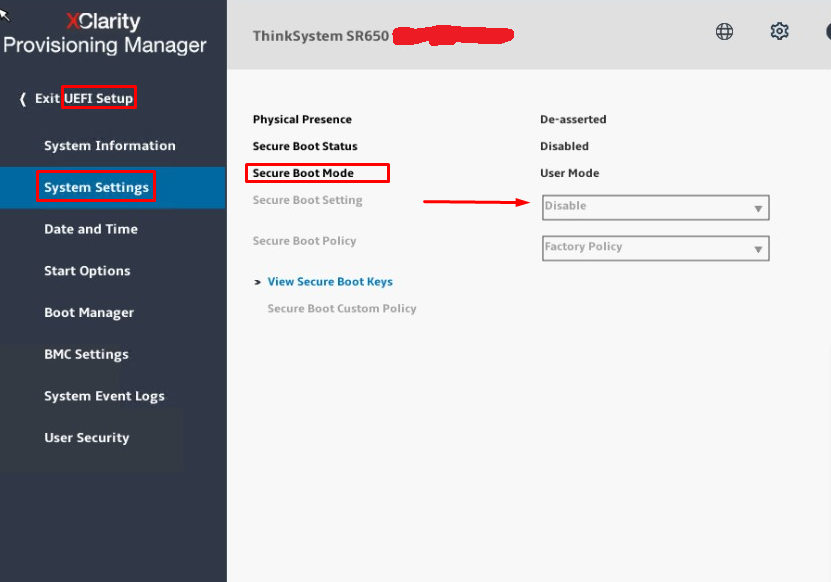
We are using Lenovo ThinkSystem SR650.For other manufacturers you may need to do it from different screens.
UEFI Setup > System Settings > Secure Boot Mode > Enable
Once enabled, the alarm condition was fixed.