In this scenario, I will describe a customer topology designed as an example.
Our customer has a location. One Disaster structure is requested by the customer.
Site information and devices ;
Turkey Site;
Device Information;
- 3 x HPe Proliant DL380 Gen11
- 1x IBM Storwize V7000
- 1x HPe StoreOnce VSA
- 2x Fortigate 200F Firewall
Network Information;
- Client 10.10.10.0/24
- Server 10.10.20.0/24
- Storage 10.10.40.0/24
- Backup 10.10.50.0/24
Germany Site;
Device Information;
- 2x HPe Proliant DL380 Gen11
- 1x HPe StoreOnce VSA
- 2x Fortigate 200F Firewall
Network Information;
- Client 10.20.10.0/24
- Server 10.20.20.0/24
- Backup 10.20.50.0/24
Let’s see how the Scenario works.
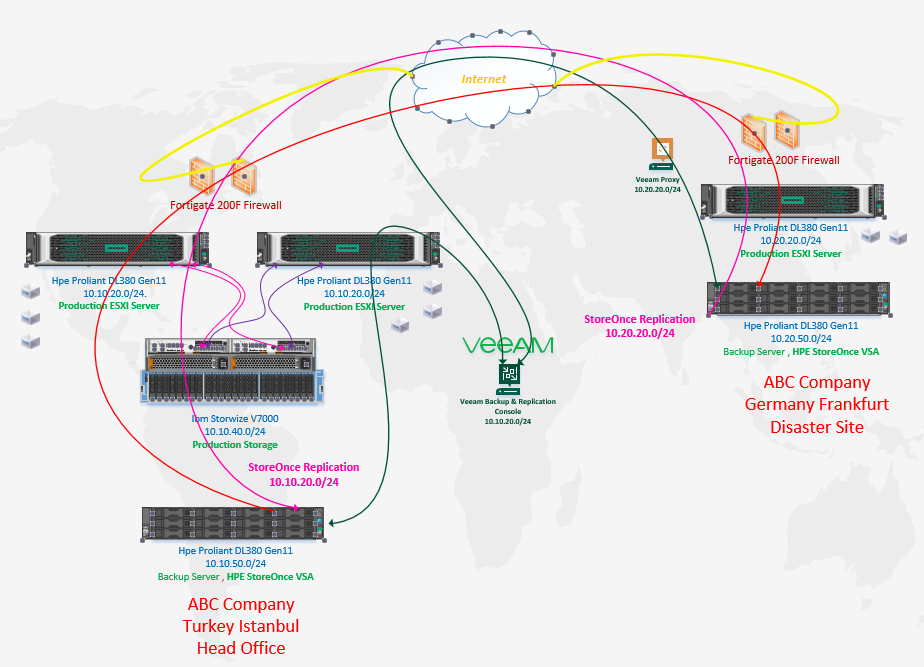
VMware esxi 8.0 is installed on three Gen11 servers in the head office. VMware vcenter 8.0 is installed to manage them.
On two Esxi 8.0 servers, the data of the virtual machines in the production environment runs on IBM Storwize Storage. On the other gen11 server, HPE Storeonce VSA has been installed, this server has a 50 TB SAS disk and is used for backup.
Likewise, there are two Gen11 servers in the disaster site, and one of them works to be opened immediately after the virtual machines in the production system are replicated with Veeam. The other Gen11 server is designed for backup purposes.
Virtual machines in the production environment are backed up on hpe storeOnce VSA every day, and are replicated to the disaster site environment with Veeam backup after the backup jobs are completed. After the Veeam Backup Replication is completed, replication is made hpestoreOnce VSA from Turkey to Germany.
Some important notes;
- There is network segmentation in this system. Server, storage and backup networks cannot be accessed from the client network.The same applies to Disaster, but there is access restriction through the firewall.
- The immutability feature was activated on HP StoreOnce and configuration was also made on the Veeam console.
- For HPE StoreOnce, a separate network block was used for the management network and a server block was used for the catalyst network. In this way, our backups will be safe as they do not access the management network. In addition, the catalyst network and Veeam console network are given from the server block so that the vlan traffic does not go to the firewall. It was made to enable operation via the switch.